AI Fraud Detection Strategies for Digital Payment Platforms
Digital payments have become the default for consumers and businesses, but the same forces driving this growth-speed, convenience, and global reach-also create fertile ground for fraud. Card-not-present attacks, account takeovers, synthetic identities, and scams are evolving faster than traditional rule-based systems can handle. As a result, AI-driven fraud detection has shifted from an experimental add-on to core infrastructure for banks, fintechs, and payment processors. This article examines how AI is actually used in fraud detection, the main techniques and architectures in production today, how leading platforms balance security with user experience, and the governance questions regulators and companies are now grappling with.
Why digital payments need AI-first fraud defenses
Fraud in digital payments is no longer a niche risk. The Federal Trade Commission in the United States has reported billions of dollars in annual losses from fraud, with card and bank transfer scams a significant part of that total. The European Central Bank and other regulators have similarly highlighted the growth of card-not-present and online banking fraud as e-commerce expands. Global card fraud losses have been estimated in the tens of billions of dollars annually by industry groups such as Nilson Report, and faster payments schemes have compressed the time available to intervene before funds leave the system.
Traditional fraud engines based on static rules-such as blocking transactions above a certain amount, from certain countries, or outside typical hours-still have value but are increasingly inadequate. Fraudsters automate testing of stolen credentials, use bots and emulators to mimic device fingerprints, and coordinate attacks across platforms and time zones. Static rules are too brittle: they either generate high false positives that annoy legitimate customers, or they are too loose and let new attack patterns slip through. AI and machine learning, by contrast, can ingest large volumes of transactional and behavioral data, detect subtle correlations, and adapt as patterns shift, making them particularly suited to high-volume fintech and digital banking environments.
For platforms operating globally or across multiple payment rails, the data itself becomes a strategic asset. When used responsibly, it allows models to spot anomalies in near real time, enrich risk scores with context, and support layered controls across cards, wallets, bank transfers, and crypto-linked rails-an increasingly common architecture covered across areas like banking, fintech, and crypto.
Core AI techniques in fraud detection
AI fraud systems for payments typically combine several machine learning approaches rather than relying on a single model. The mix depends on the platform's size, data maturity, regulatory obligations, and risk appetite.
Supervised learning remains the backbone for many providers. Historical transactions are labeled as fraudulent or legitimate, and algorithms such as gradient-boosted trees, random forests, and increasingly deep learning architectures learn to classify new transactions. Companies like Visa, Mastercard, and American Express have publicly discussed using such techniques in their risk platforms, training models on billions of transactions to compute near-instant fraud scores. These models can factor in hundreds of features-from merchant category and device attributes to time-of-day patterns and historical behavior-far beyond what hand-written rules can manage.
Unsupervised and semi-supervised learning are essential for detecting new attack types that lack historical labels. Clustering, density estimation, and autoencoders can identify outliers or unusual spending patterns without needing explicit examples of fraud. For instance, if a new type of mule account behavior emerges, unsupervised models may flag it as anomalous even before investigators have labeled specific cases. This is especially useful for emerging rails like real-time payments and open banking APIs, where patterns can change quickly.
Graph-based methods are increasingly important as fraud becomes more networked. Graph neural networks and related algorithms model relationships among cards, devices, IP addresses, merchants, and accounts. By analyzing these connections, platforms can identify fraud rings, synthetic identity webs, and mule networks that might appear benign when viewed transaction by transaction. Firms such as FICO and several specialist vendors have invested in graph analytics for precisely this reason.
On top of these, many providers use reinforcement learning or bandit algorithms to optimize decision strategies over time. Rather than only predicting risk, the system learns which combination of actions-approve, decline, challenge with step-up authentication, or hold for review-maximizes long-term value by balancing fraud losses against customer friction and operational cost. This is particularly relevant for high-volume e-commerce gateways and marketplaces.
Data foundations: what effective fraud models actually use
The performance of AI fraud detectors depends at least as much on data quality and feature engineering as on model choice. Payment platforms that treat fraud as a first-class data problem tend to outperform those that simply plug in an off-the-shelf model.
At the core is transactional data: amount, currency, merchant or payee, channel (web, app, POS), card or account details, and timestamps. But leading platforms enrich this with a wide array of contextual signals. Device intelligence-such as browser fingerprints, operating system versions, jailbreak or root status, and sensor data from mobile devices-is commonly used to distinguish genuine users from bots or emulators. Behavioral biometrics add another layer, capturing how a user types, swipes, or moves through a checkout flow. Companies like BioCatch and BehavioSec have built businesses around such signals, which can be especially powerful against account takeover.
Location and network data are similarly critical. IP geolocation, VPN and proxy detection, and mobile network attributes help identify suspicious access patterns. For instance, a login from a new device in one country followed minutes later by a card-not-present transaction from another may be a strong red flag. Payment platforms often supplement this with third-party threat intelligence from providers such as Recorded Future or Kaspersky, which track known bad IP ranges, malware signatures, and botnet activity.
For digital banks and neobanks, internal account behavior is another rich source. Transaction histories, salary patterns, peer-to-peer transfers, and interactions with savings or credit products allow models to build individualized baselines. Abrupt deviations-such as sudden large outgoing wires or unusual merchant types-can be detected more reliably when the system understands what "normal" looks like for each customer. This overlaps with broader banking risk and AML efforts, often discussed alongside fraud in economy and business coverage.
Finally, labels and feedback loops are crucial. Fraud teams, chargeback outcomes, customer disputes, and law enforcement referrals all generate labels that update model training data. Platforms with tight integration between operations and data science can shorten the time between a new fraud pattern emerging and the model learning to detect it.
Real-time decisioning and layered defenses
Digital payment platforms must make risk decisions in milliseconds, often under strict service-level agreements with merchants and partner banks. This makes the architecture of AI fraud systems as important as the models themselves.
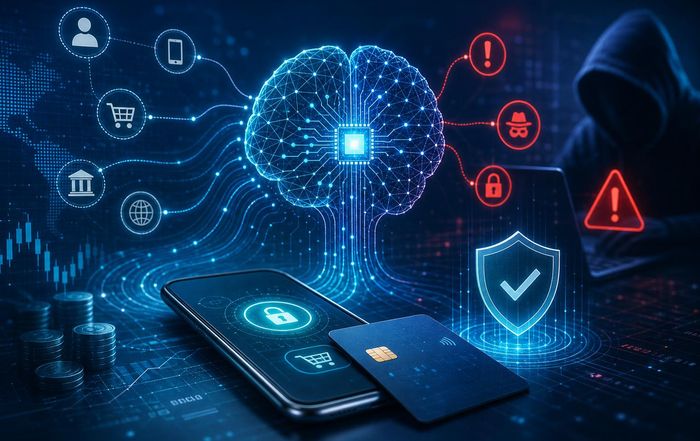
Most modern providers deploy models in a streaming, real-time scoring pipeline. When a transaction request arrives-whether a card authorization, a wallet payment, or an instant bank transfer-the risk engine assembles relevant features from multiple sources: customer profile, historical transactions, device data, and external intelligence. The AI model then outputs a risk score, typically a probability that the transaction is fraudulent. A policy layer transforms this score into an action: approve, decline, step-up authentication, or route to manual review.
This policy layer is where AI and rules often coexist. Hard rules remain valuable for clear, non-negotiable conditions, such as blocking transactions from sanctioned entities under regimes like OFAC in the United States or EU sanctions lists. AI scores handle more nuanced judgments, especially around consumer behavior and merchant-specific risk. Platforms can also apply different thresholds by geography, payment type, and customer segment, reflecting local regulations and business priorities across regions such as Europe, Asia, and North America.
Layered controls are essential. Authentication mechanisms like EMV 3-D Secure, biometric login, and strong customer authentication under frameworks such as the EU's PSD2 provide front-end defenses, while AI models operate in the background to spot anomalies even when credentials appear valid. Device binding, risk-based authentication, and transaction signing help limit the impact of credential theft. For instant payment schemes where funds may be irrevocable, some banks and fintechs now pre-screen payee details and historical behavior before allowing new beneficiaries or high-risk transfers.
These layers must also account for security beyond fraud, including malware, phishing, and social engineering. While fraud detection and cybersecurity are distinct disciplines, they increasingly share signals and tooling. Readers exploring broader cyber topics can find related coverage in security and ai sections.
Balancing fraud prevention with user experience
A central tension in digital payments is the trade-off between security and friction. Overly aggressive fraud controls can cause false declines, abandoned carts, and customer churn; too much leniency exposes platforms to losses and reputational damage. AI is often positioned as a way to break this trade-off, but the reality is more nuanced.
Risk-based authentication is one of the main strategies for balancing these concerns. Rather than applying strong authentication to every transaction, platforms use AI scores to determine when additional checks are necessary. Under PSD2, for example, the concept of "transaction risk analysis" allows payment service providers to exempt low-risk payments from strong customer authentication if their fraud rates stay below defined thresholds. This has driven investment in more accurate, explainable fraud models among European acquirers and issuers.
Customer segmentation is another lever. Longstanding customers with stable behavior and verified identities may enjoy smoother experiences, while new or previously dormant accounts face tighter scrutiny. Some neobanks use progressive limits, raising daily transfer caps as the system gains confidence in a customer's behavior. Marketplaces and gig platforms often apply similar logic to sellers or service providers.
However, AI is not a silver bullet. Bias and unfair treatment can emerge if training data reflects historical discrimination or if proxy variables correlate with protected characteristics. Regulators such as the European Banking Authority, the Financial Conduct Authority in the UK, and agencies in other major markets have signaled expectations that firms monitor AI models for discriminatory impacts and ensure that fraud controls do not unfairly exclude certain groups. This is part of a broader regulatory conversation about AI governance in finance, including the EU's AI Act and various national AI policy frameworks.
To maintain trust, some platforms now invest in customer-facing transparency. When a transaction is declined or challenged, they provide clearer explanations and streamlined ways to confirm legitimacy. This is not only a user-experience issue but also helps gather faster feedback for model retraining.
Regulatory, ethical, and governance considerations
AI-driven fraud detection sits at the intersection of payments regulation, data protection, and emerging AI governance frameworks. Digital payment platforms must navigate multiple regimes simultaneously, especially when operating across borders.
Data protection and privacy laws such as the GDPR in Europe and the CCPA/CPRA in California impose strict requirements on how personal data is collected, processed, and shared. Fraud prevention is typically recognized as a legitimate interest or legal obligation, but firms must still minimize data collection, ensure appropriate retention periods, and protect sensitive attributes. Profiling and automated decision-making rules under GDPR require that individuals be informed about the existence of automated decisions with significant effects, and in some cases provide the right to human review.
Financial crime regulations add another layer. Anti-money-laundering (AML) and counter-terrorist financing rules enforced by bodies like the Financial Action Task Force (FATF) expect institutions to adopt risk-based approaches, which increasingly involve AI. However, regulators also stress that ultimate responsibility cannot be outsourced to algorithms. Firms must understand how their models work, validate performance, and maintain documentation. In some jurisdictions, supervisors now ask to review model governance frameworks, including independent validation, back-testing, and monitoring for drift.
The rise of general-purpose AI has prompted further scrutiny. The European Union's AI Act categorizes AI used in credit scoring and certain financial services as high-risk, subjecting them to requirements around risk management, data quality, transparency, and human oversight. While fraud detection is not always explicitly listed, many institutions treat it as high-risk due to its impact on customers and systemic importance. Central banks and supervisors-from the Bank of England and European Central Bank to the Monetary Authority of Singapore-have published guidance or discussion papers on responsible AI in finance, emphasizing explainability, accountability, and resilience.
Ethically, platforms must balance aggressive fraud reduction with fairness and due process. Over-reliance on opaque models can lead to "de-risking," where certain customer segments or geographies are effectively excluded from digital payments. This has broader implications for financial inclusion and the digital economy, themes often explored in world and education coverage. Boards and executives are increasingly expected to oversee AI ethics, not just compliance checklists.
Emerging threats and the role of generative AI
Fraud tactics evolve alongside defenses, and generative AI has become both a tool for attackers and a potential asset for defenders. Voice cloning, deepfake video, and sophisticated phishing emails lower the cost of social engineering and business email compromise. Criminals can generate convincing messages in multiple languages, impersonate executives, or simulate customer voices to bypass call-center verification. Law enforcement agencies and cybersecurity firms, including Europol and major security vendors, have warned about these trends.
For digital payment platforms, this raises the stakes around identity verification and customer authentication. Knowledge-based questions and simple voice recognition are increasingly vulnerable. Multi-factor authentication that combines device binding, cryptographic proofs, and behavioral biometrics becomes more important. AI models that detect anomalies in conversational patterns or call metadata may help identify synthetic voices or scripted interactions, but these defenses are still maturing.
On the defensive side, generative AI can assist fraud analysts by summarizing complex case histories, suggesting follow-up questions, or drafting communications to customers and partner banks. Large language models can help triage alerts, extract entities from unstructured evidence, and surface similar cases from historical data. However, these tools must be carefully constrained and audited to avoid hallucinations and privacy breaches.
Synthetic data is another area of experimentation. Some institutions use AI to generate realistic but non-identifiable transaction data for model training and testing, especially when sharing data across teams or borders is restricted. While promising, synthetic data must be validated rigorously to ensure it preserves relevant statistical properties without leaking sensitive information. Organizations such as NIST in the United States and academic centers focused on privacy-preserving machine learning are active in this research space.
Practical strategies for payment platforms adopting AI fraud tools
For founders, product leaders, and risk executives in digital payments, the strategic question is not whether to use AI for fraud detection, but how to do so in a way that is effective, compliant, and sustainable.
A first step is building a solid data and feature platform. Without clean, well-structured data and reliable event tracking across channels, even the most advanced models will underperform. Many fintechs invest early in centralized data lakes or warehouses, stream processing frameworks, and feature stores that enable consistent feature definitions across training and production. This data foundation also supports adjacent use cases such as credit risk, personalization, and operational analytics, relevant to areas like stock-exchange and broader business strategy.
Next comes deciding between building in-house models, using vendor solutions, or a hybrid approach. Large banks and global payment processors often maintain internal data science teams and proprietary models, sometimes supplemented by third-party tools for device intelligence or behavioral biometrics. Smaller platforms may rely more heavily on vendors, integrating risk APIs from specialist providers or gateways. In either case, it is important to retain enough internal expertise to understand model behavior, tune thresholds, and respond quickly to new threats.
Model governance should not be an afterthought. Clear processes for model development, validation, deployment, and monitoring are essential, including documentation of assumptions, limitations, and performance metrics. Many institutions adopt frameworks inspired by model risk management guidelines from regulators such as the Federal Reserve in the United States or equivalent bodies elsewhere, even when not strictly required. Regular back-testing, stress testing with simulated attack scenarios, and monitoring for data drift help ensure that models remain effective over time.
Collaboration is another strategic lever. Industry information-sharing groups, card network risk programs, and public-private partnerships allow platforms to exchange intelligence on emerging fraud patterns. Organizations like FS-ISAC provide mechanisms for sharing threat information among financial institutions globally. While competitive and privacy concerns limit what can be shared, coordinated responses can raise the cost for fraudsters.
Finally, platforms should invest in people and culture. Skilled fraud analysts, data scientists, and engineers who understand both payments and machine learning are critical. Training frontline staff to recognize patterns, interpret model outputs, and escalate unusual cases can significantly enhance AI tools. Educating customers about safe payment practices, scam awareness, and the meaning of security prompts can also reduce fraud exposure-linking operational strategy with broader themes in jobs and environment when considering the wider socio-economic impact of secure digital finance.
Where AI fraud detection is heading?
AI-driven fraud detection for digital payment platforms is moving toward more integrated, context-aware, and collaborative models. Rather than isolated engines bolted onto specific rails, risk intelligence is increasingly shared across cards, bank transfers, wallets, and even crypto interfaces, reflecting how consumers and businesses actually move money. Real-time graph analytics and cross-institution data pooling-subject to privacy and competition constraints-could further strengthen defenses against organized crime and large-scale scams.
At the same time, regulatory expectations around explainability, fairness, and resilience will likely tighten. Platforms that can demonstrate robust model governance, transparent decisioning, and careful handling of personal data will be better positioned to innovate while maintaining trust. As generative AI reshapes both attack and defense, the emphasis will shift from static controls to adaptive, intelligence-driven systems where human expertise and machine learning reinforce each other.
For digital payment platforms, the strategic challenge is to treat AI fraud detection not as a one-off technology project, but as a continuous capability-deeply embedded in product design, compliance, and customer experience. Those that get this right will be better equipped to support the next wave of innovation in fintech, digital banking, and the broader digital economy.
